Social Engineering on Corporate Chat
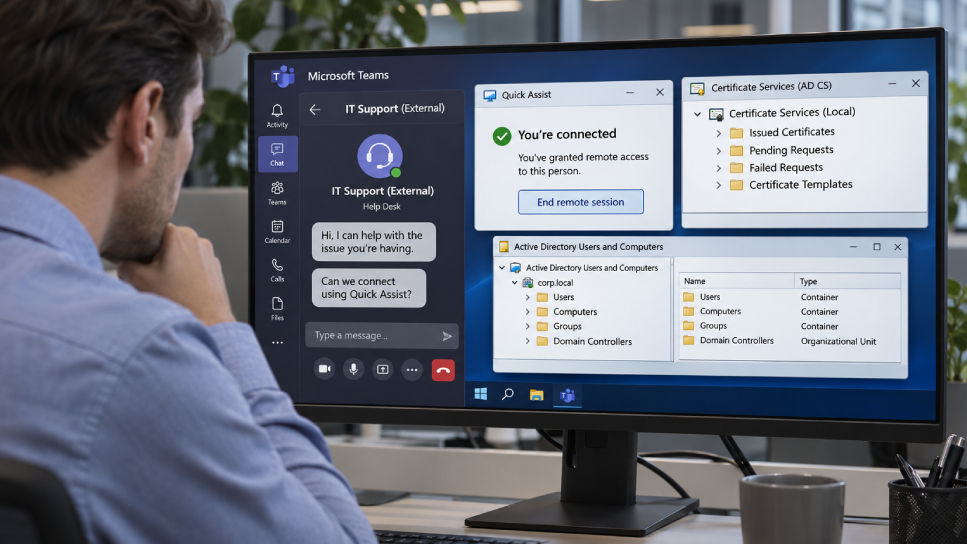
Attackers are impersonating IT support personnel on Microsoft Teams to trick corporate employees into handing over remote control of their computers. According to a security report from Microsoft, threat actors used this initial remote access to exploit weak configurations in Active Directory Certificate Services (AD CS).
How the Attack Works
Active Directory Certificate Services is a server role that allows organisations to issue and manage digital certificates used for identity authentication and secure communication. By exploiting insecure AD CS settings, the attackers successfully obtained login certificates for privileged accounts, including an account for a domain controller.
Microsoft confirmed that it investigated two separate intrusions involving this social engineering tactic, with at least one incident leading to the theft of corporate data.
What It Means for Security Teams
This tactic highlights how attackers combine direct social engineering with internal system misconfigurations. Organisations using Microsoft Teams and Active Directory should ensure remote access policies are strictly enforced and review their certificate service deployment settings to prevent unauthorised access.


