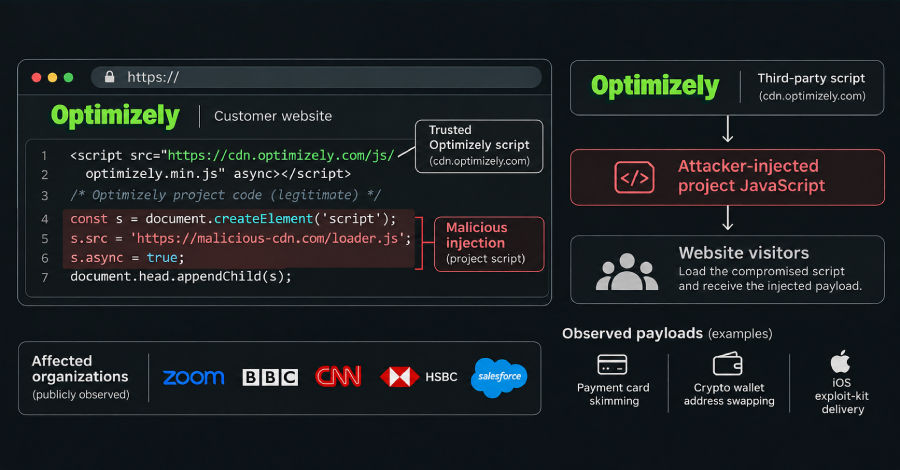
An attacker exploited a flaw in Optimizely Web Experimentation to plant malicious code inside scripts that customer websites load from the service, Optimizely said. Visitors to sites run by at least 178 organisations, among them CNN, the BBC and Zoom, received the code the previous day, according to Report URI, a firm that monitors the scripts websites run.
What the hijack involved
Optimizely Web Experimentation is a service companies use to test page changes, such as different headlines or button placements, by loading Optimizely's scripts into their own pages. Because those scripts run inside the customer's site, anyone who can alter them can reach every visitor to that site.
The report describes the injected code as a card skimmer and iOS exploit kits. A card skimmer is malicious code that quietly captures payment card details as shoppers type them into a checkout page.
What is not yet established
The available account does not say how the flaw was exploited, how long the malicious code stayed live, whether any card data was captured, or what Optimizely has done beyond acknowledging the issue. Those questions matter most for the 178 organisations whose visitors were exposed.


