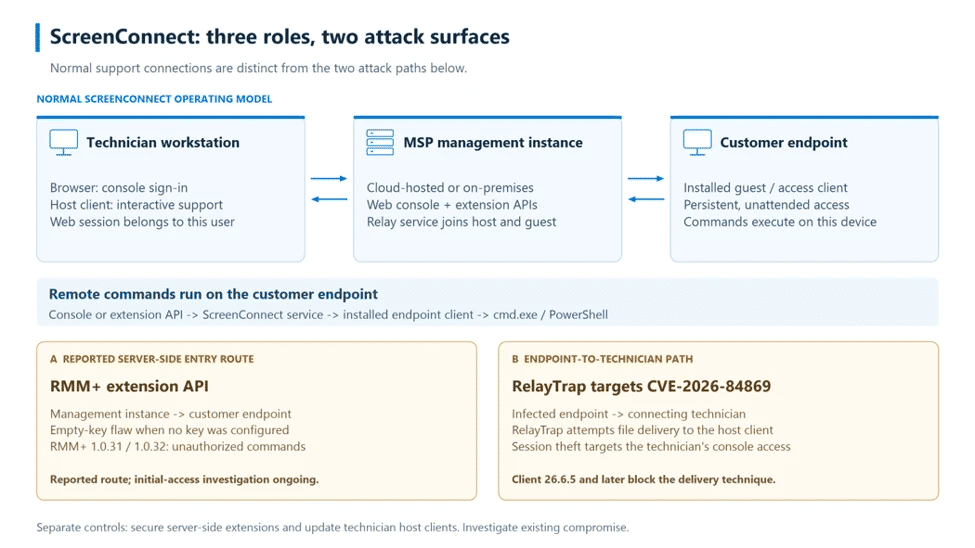
Microsoft's security research team has published an analysis of a tool it calls SCKit, which it says abuses ScreenConnect to obtain unauthorised remote access and to target technician sessions. The Microsoft Security Blog post, credited to Sagar Patil and Jeremiah Jasmin and dated 13 November 2026, also sets out the attack chain, mitigations and hunting guidance for Microsoft Defender XDR.
What ScreenConnect is
ScreenConnect is a remote monitoring and management product from ConnectWise. IT support teams use tools of this kind to connect to a customer's computer remotely, troubleshoot problems and run maintenance without travelling to the machine. That legitimate function is what makes the abuse notable: the same remote access capability that helps a support desk can, in the wrong hands, give an intruder a foothold on a system.
Sessions worth stealing
Microsoft's title points to technician sessions as a target. Technician accounts typically carry broad administrative rights over the systems they support, which is general context for why such sessions attract attackers rather than a specific finding from the post.
What remains unknown
Microsoft's summary does not identify who is behind SCKit, which sectors or countries have been affected, how many organisations were involved, or whether the activity is ongoing. VANTIX was able to review only the published summary, not the full technical write-up, so the attack chain and mitigation steps are not detailed here.
Defender XDR and hunting
Microsoft Defender XDR is Microsoft's extended detection and response platform, which correlates signals from endpoints, identity, email and cloud applications in one place. Hunting guidance refers to instructions for searching collected security telemetry for traces of an intrusion, rather than waiting for an automated alert. Organisations that use ScreenConnect and Defender XDR should read the original post for the specific indicators and mitigations Microsoft describes.


