What happened
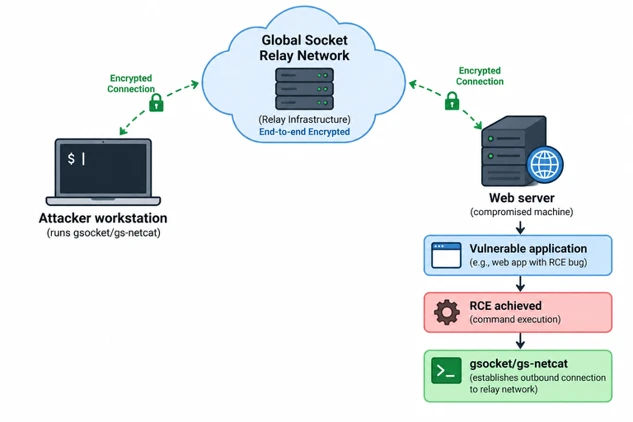
Microsoft Security researchers say threat actors are deploying GSocket on compromised Linux servers to maintain encrypted remote access after the original vulnerability has been patched. The activity is described as stealthy command-and-control, or C2, which lets attackers communicate with compromised systems.
The finding appears in a Microsoft Security Blog post by Yash Gund, Sumith Maniath and Microsoft Security Research, published on 11 November 2026.
What Microsoft says defenders should do
According to the publisher’s summary, the post explains how to detect, investigate and remediate this activity. The summary does not include specific detection rules, remediation steps, or the number of affected servers.
What remains unknown
The summary does not name the vulnerability that was patched, identify the threat actors involved, or say how many servers were compromised. It also does not establish any connection to Nigeria or other African markets, so this is reported as a global development. VANTIX cannot confirm details beyond the publisher’s summary.


